Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 DeepSeek
 Muse+22 moreClaude CodeCursorCodex CLIDeepSeekMuse
 Dots
 Manus
 Grok
 Grok Bot+18 agents
Secrets Exposure Audit
Find leaked credentials across history, logs and bundles, triage real exposure, then rotate and prevent.
$12

Secrets Exposure Audit
Example session with this skill installed
We are about to open-source our repo next month. Here is our git history export, CI config and a list of active provider keys. Find what would leak and tell me what to rotate.
- Read your context and instructions
- Compiled the secrets exposure audit
Worked example — illustrative data.
Secrets audit: monorepo
Verdict
14 findings, 3 live, 1 public. Highest risk: a live Stripe key committed in a .env file on 3 March, still valid. Rotate before anything else.
Findings
| ID | Location | Type | Live | Exposure | Action |
|---|---|---|---|---|---|
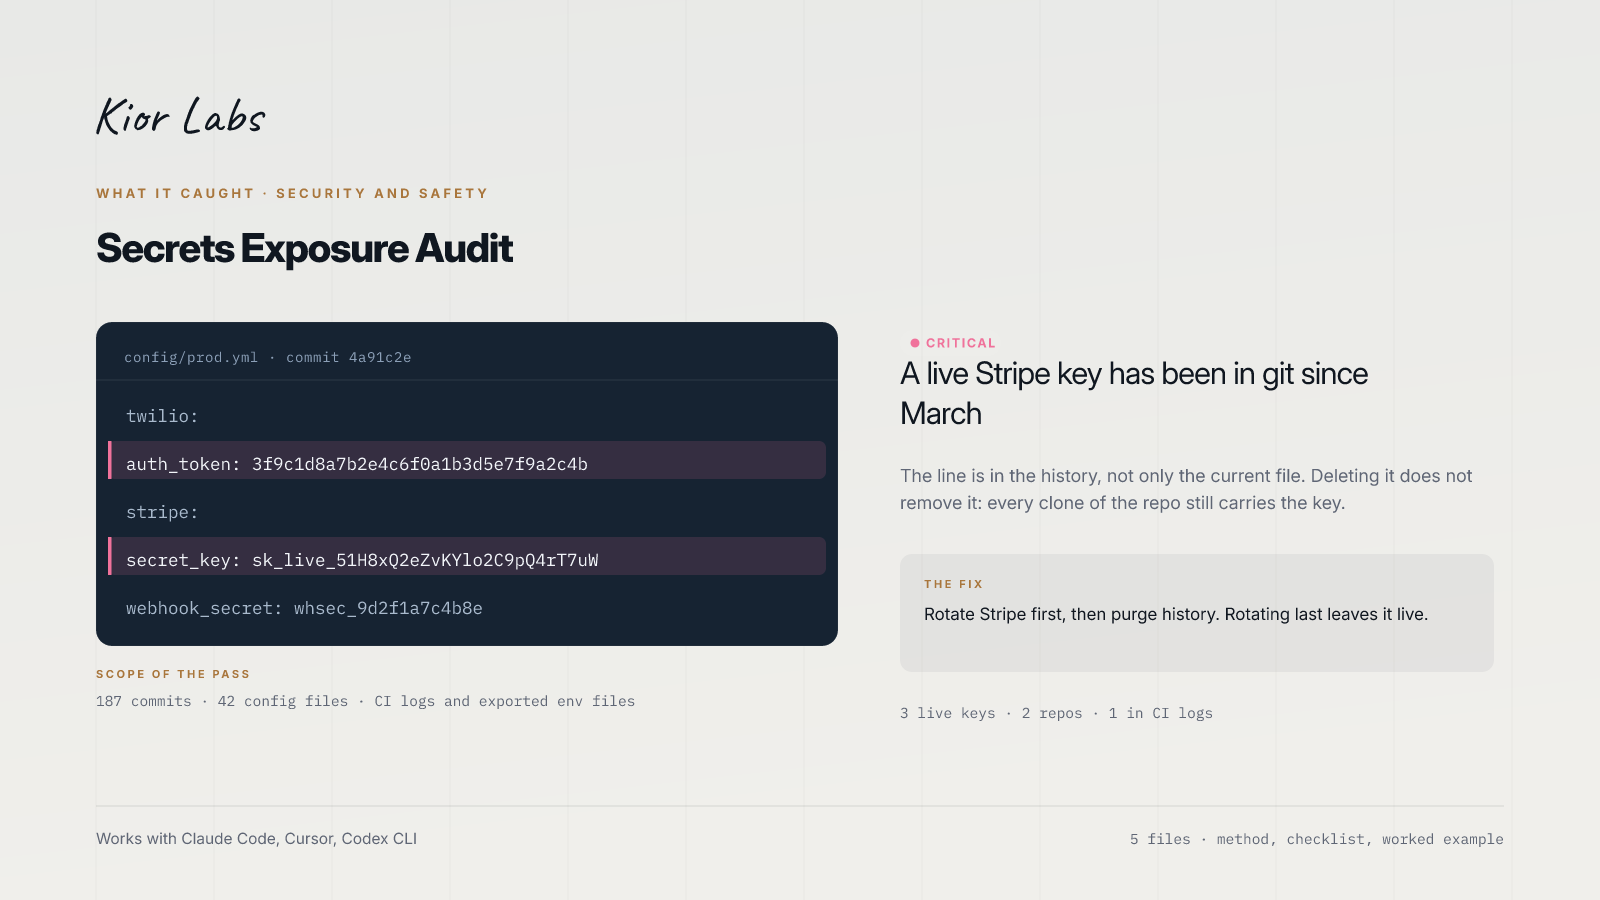
| S1 | .env, commit a1b2c3 (3 Mar) | Stripe live key | yes | public via fork | rotate now |
| S2 | CI log, build 4412 | AWS access key | yes | private, 12 viewers | rotate today |
| S3 | client bundle app.js | Mapbox token | yes | public | restrict origins |
| S4 | tests/fixtures.json | OpenAI key (fake) | no | public | remove, allowlist noise |
| S5 | notebook output | DB URL with password | expired | private | rotate and purge |
Exposure timeline
S1 entered 3 Mar, removed from HEAD 14 Apr, still in history and two forks.
Usage check
Stripe logs show 4 requests from an unknown IP on 2 May. Escalated as an incident.
Rotation log
| Credential | Issued | Deployed | Revoked | Verified |
|---|---|---|---|---|
| Stripe live | 12 Nov | 12 Nov | 12 Nov | pass |
| AWS access key | 12 Nov | 12 Nov | 12 Nov | pass |
Prevention
Secret scanning and push protection on all repos; CI blocks on new findings; runtime secrets from the manager only; 90-day rotation where short-lived is impossible.
Residual risk
Two long-lived third-party keys remain; migration scheduled for Q1.
Connects securely to your tools. The creator never sees your data.
About this skill
Leaked API key audit for code, git history, configs, CI logs and build output, with a rotation order and a prevention plan.
Use this skill when:
- find leaked API keys
- a key was committed or pasted into a log
- prepare for a security audit or SOC 2 review
- rotate credentials safely
Who it's for: Backend and platform teams after an exposure, or before an audit.
Example request
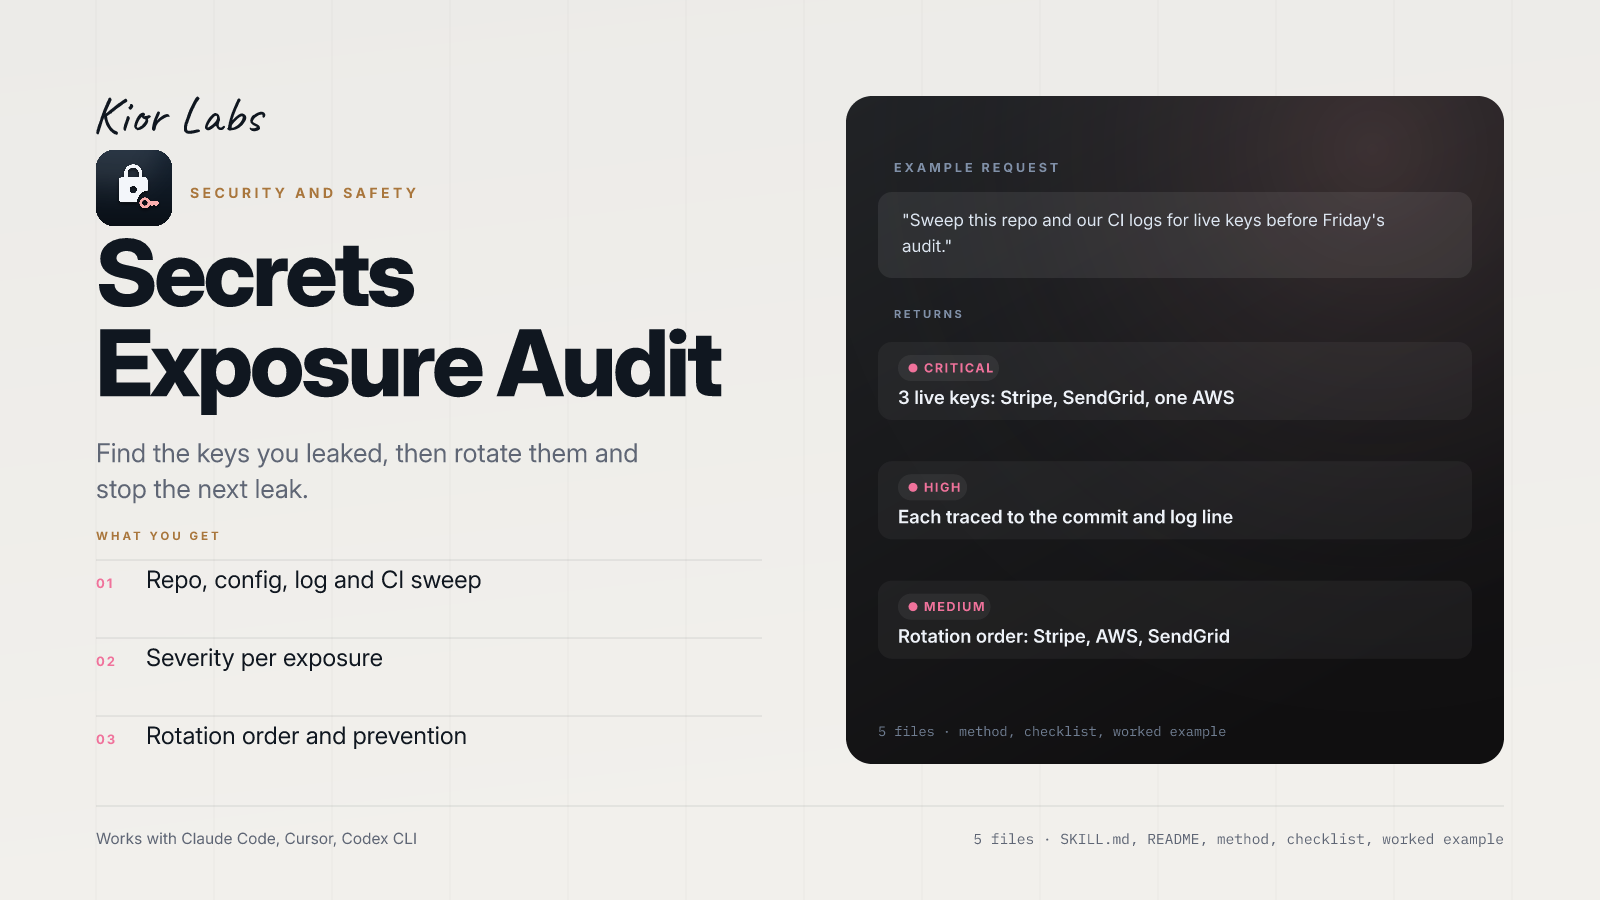
Sweep this repo and our CI logs for live keys before Friday's audit.
What the example returns
- 3 live keys: Stripe, SendGrid, one AWS
- Each traced to the commit and log line
- Rotation order: Stripe, AWS, SendGrid
In the package: five files — SKILL.md with the trigger and workflow, README.md, references/METHOD.md (the full method), references/CHECKLIST.md (the pass/fail gate) and examples/EXAMPLE.md (a worked run you can copy).
Works with Claude Code, Cursor, Codex CLI and any agent that reads SKILL.md. Plain markdown: no API key, no account, no network access.
Find more skills like this on the Claude Skills Marketplace, the Codex Skills Marketplace and the Gemini Skills Marketplace, or browse Claude Skills for DevOps & Cloud.
Requires manual verification of findings to filter false positives. Does not automatically execute API calls for key revocation. Scope limited to text-based surfaces and log archives.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before buying a skill.
Reviews
No reviews yet
Be one of the first to try it. Every listed skill goes through the trust checks below.
Security scanned
Checked by our 8-point scan before listing
Fresh listing
Recently published to Agensi
Money-back guarantee
Doesn't do what its page promises? You get your money back.
Trust & safety
Security scan
Security scan passed 2 days ago
Permissions
Works only from files and logs you provide. No network calls, no credentials, and secrets are shown as prefixes only.