Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 DeepSeek
 Muse+22 moreClaude CodeCursorCodex CLIDeepSeekMuse
 Dots
 Manus
 Grok
 Grok Bot+18 agents
MCP OAuth Implementer
Move a remote MCP server from a shared API key to OAuth 2.1: discovery, audience, scopes and tests.
$19

MCP OAuth Implementer
Example session with this skill installed
Our MCP server is internet-facing and uses one API key for everyone. Clients keep failing to authenticate. Move us to OAuth and tell me what to test.
- Read your context and instructions
- Compiled the mcp oauth implementer
Worked example — illustrative data.
OAuth implementation: orders MCP server
Current state
One static key in an environment variable, shared by all users, no scopes, no expiry. Internet-facing behind a proxy.
Target flow
Client -> 401 with resource_metadata -> fetch metadata -> discover AS -> OAuth 2.1 + PKCE -> bearer token with audience https://mcp.example.com -> tool call.
Metadata
{ "resource": "https://mcp.example.com",
  "authorization_servers": ["https://auth.example.com"],
  "scopes_supported": ["orders:read","refunds:write","workspace:export"] }
Validation
JWKS cached 10 minutes with rotation; iss, aud, exp, nbf checked with 60s skew; scope checked per tool; passthrough tokens rejected.
Scope map
| Tool | Scope |
|---|---|
| search_orders | orders:read |
| get_order | orders:read |
| refund_order | refunds:write |
| export_workspace | workspace:export |
Migration
- Accept key and OAuth for one release; log identity per call.
- Rotate all keys to short-lived tokens.
- Announce removal date (30 days).
- Remove key support.
Tests
| Test | Result |
|---|---|
| No token returns 401 + metadata | pass |
| Wrong audience rejected | pass |
| Expired token rejected | pass |
| Insufficient scope returns 403 | pass |
| Cross-tenant read blocked | pass |
| Revocation within cache TTL | pass (10 min) |
Residual risk
Revocation takes up to 10 minutes because of JWKS caching; acceptable for read tools, documented for refunds.
Connects securely to your tools. The creator never sees your data.
About this skill
OAuth 2.1 for MCP servers: discovery metadata, audience validation, scopes mapped to tools, and the tests that prove it works.
Use this skill when:
- add OAuth to an MCP server
- set up MCP authentication and scopes
- a remote MCP server needs tokens
- debug 401s from an MCP client
Who it's for: MCP server authors shipping to other people's agents.
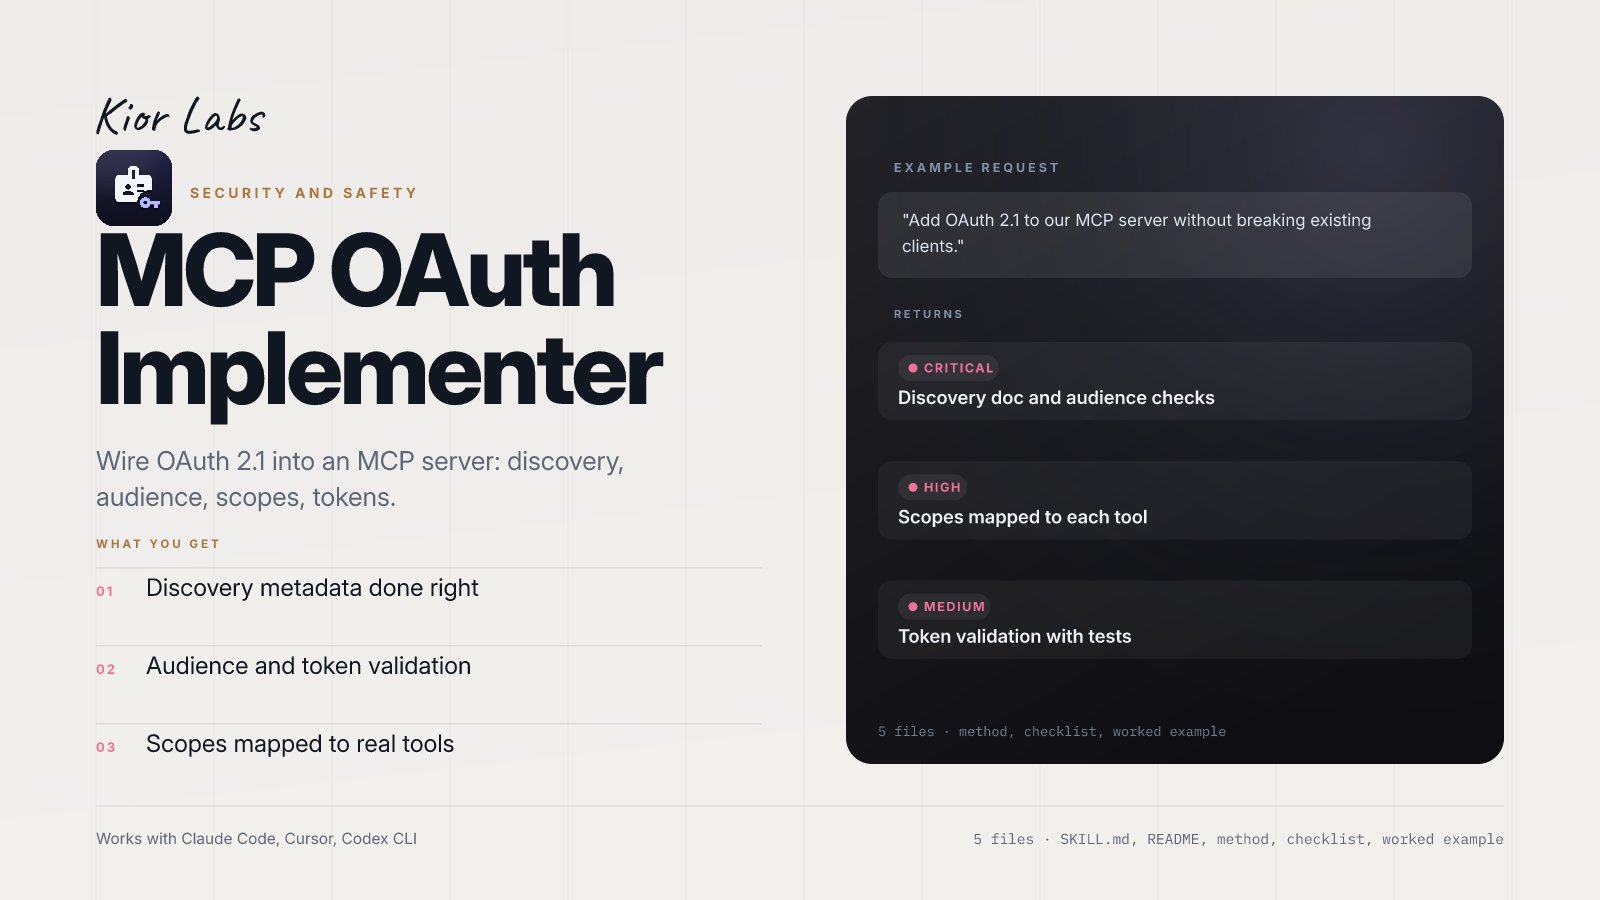
Example request
Add OAuth 2.1 to our MCP server without breaking existing clients.
What the example returns
- Discovery doc and audience checks
- Scopes mapped to each tool
- Token validation with tests
In the package: five files — SKILL.md with the trigger and workflow, README.md, references/METHOD.md (the full method), references/CHECKLIST.md (the pass/fail gate) and examples/EXAMPLE.md (a worked run you can copy).
Works with Claude Code, Cursor, Codex CLI and any agent that reads SKILL.md. Plain markdown: no API key, no account, no network access.
Find more skills like this on the Claude Skills Marketplace, the Codex Skills Marketplace and the Gemini Skills Marketplace, or browse Claude Skills for Security.
Focuses on resource server implementation. Does not provide code for building a custom Authorization Server. Assumes the server is internet-facing or reachable by the client.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before buying a skill.
Reviews
No reviews yet
Be one of the first to try it. Every listed skill goes through the trust checks below.
Security scanned
Checked by our 8-point scan before listing
Fresh listing
Recently published to Agensi
Money-back guarantee
Doesn't do what its page promises? You get your money back.
Trust & safety
Security scan
Security scan passed 2 days ago
Permissions
Produces an implementation plan from code and configuration you provide. No network calls, no credentials.