More screenshots
Works with the AI Agents you already use
 Claude Code
 Cursor
 Codex CLI
 DeepSeek
 Muse+22 moreClaude CodeCursorCodex CLIDeepSeekMuse
 Dots
 Manus
 Grok
 Grok Bot+18 agents
http security headers checker
Grade saved HTTP response headers against OWASP Secure Headers — HSTS, CSP, cookies, CORS and leaky Server banners, with a 0–100 score.
$5

http security headers checker
Example session with this skill installed
I just ran curl -I on my staging site and saved it to staging-headers.txt. Can you audit these for security issues and give me the report in markdown?
- Read your context and instructions
- Compiled the http security headers
- Generated the document
I have analyzed the headers in staging-headers.txt against the OWASP Secure Headers project standards. The audit found 3 HIGH severity issues related to missing transport security and content isolation.
HTTP Security Audit: staging-headers.txt
| Header | Status | Severity | Recommendation |
|---|---|---|---|
| Strict-Transport-Security | MISSING | HIGH | max-age=63072000; includeSubDomains; preload |
| Content-Security-Policy | MISSING | HIGH | Define a policy, e.g., default-src 'self'; |
| X-Frame-Options | MISSING | HIGH | DENY or SAMEORIGIN to prevent clickjacking. |
| X-Content-Type-Options | PASS | OK | Already set to nosniff. |
| Server | LEAK | LOW | Value nginx/1.18.0 (Ubuntu) exposes OS and version. |
| Referrer-Policy | MISSING | LOW | strict-origin-when-cross-origin |
Detailed Findings
- Missing HSTS: The site does not enforce HTTPS at the browser level. This allows for SSL stripping attacks.
- Missing CSP: No Content Security Policy is defined, leaving the site vulnerable to XSS and data injection.
Information Leakage: The Server header reveals specific version numbers. Attackers use this to target known CVEs for Nginx 1.18.0.
Next steps
- Update your Nginx configuration with the recommended HSTS and CSP values.
- Set
server_tokens off;in your Nginx config to hide the version string. - Run the tls server config auditor to check your cipher suites and protocol versions.
1793174890073-dz6t.png
PDF · document
Example file from a real run - the skill writes it into your workspace.
Connects securely to your tools. The creator never sees your data.
About this skill
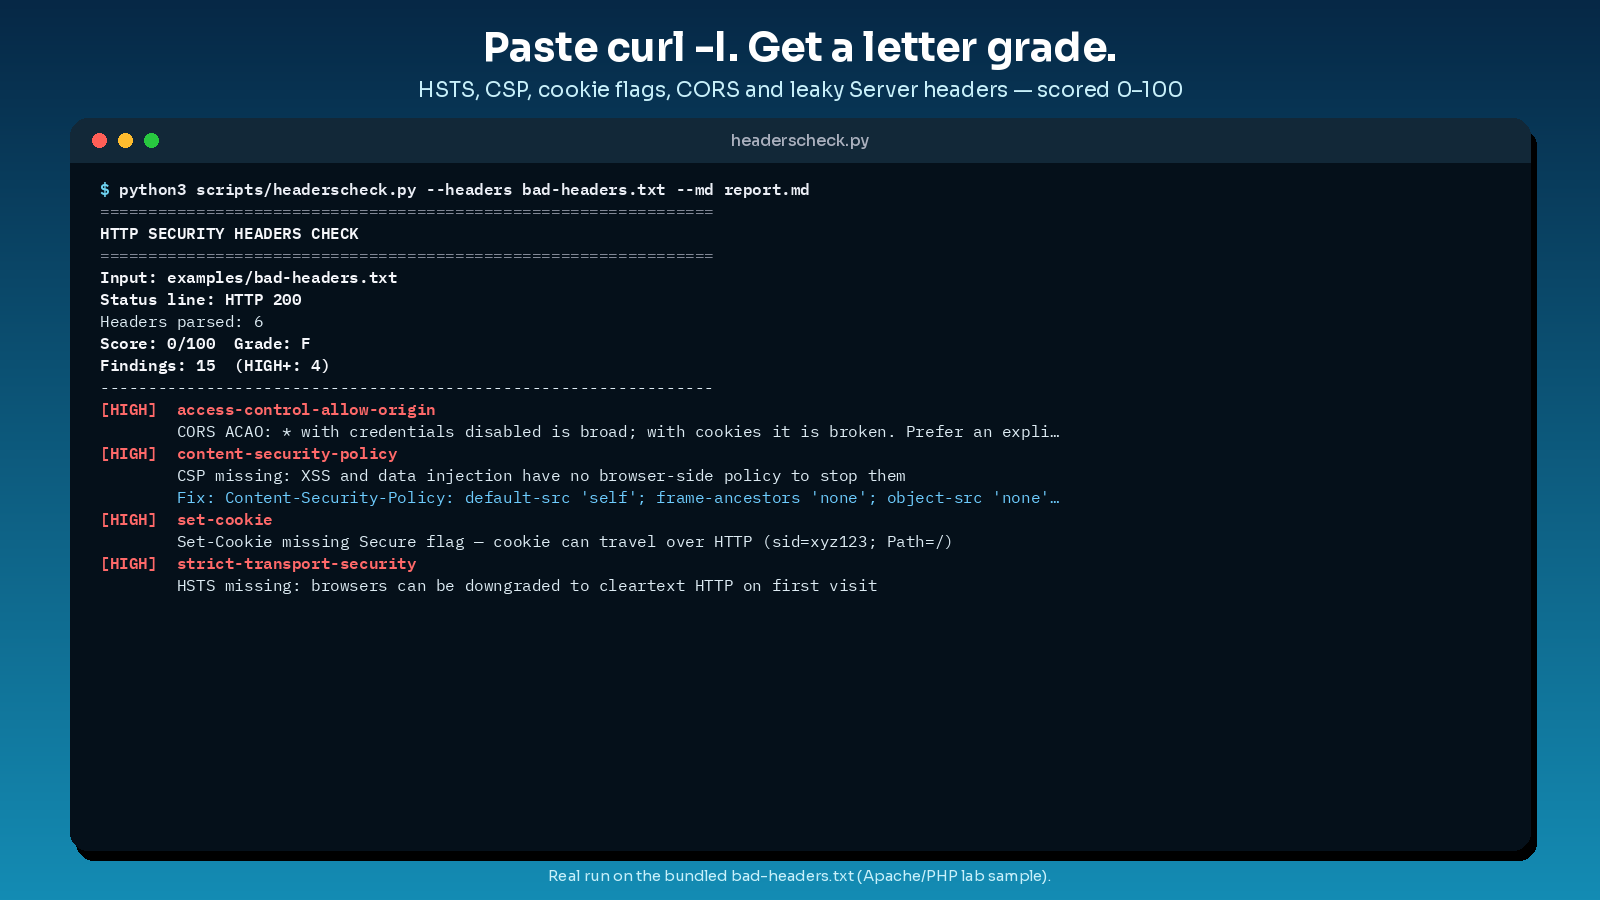
Paste curl -I output. Get a letter grade and the exact headers to add.
Security scanners keep flagging missing CSP, HSTS and cookie flags. This skill grades a saved HTTP response (curl -I, curl -v, or DevTools copy) against OWASP Secure Headers recommendations and tells you exactly what to add.
What it does
- Parses raw response headers or curl -v transcripts (strips the
<noise) - Scores HSTS, CSP, X-Content-Type-Options, X-Frame-Options / frame-ancestors, Referrer-Policy, Permissions-Policy, COOP, CORP
- Checks Set-Cookie for Secure, HttpOnly and SameSite; flags ACAO: * and leaky Server / X-Powered-By
- Writes Markdown + CSV reports; exit 0 when there are no HIGH findings
Who it's for
Web developers, MSPs and small-business IT who want a repeatable offline headers check their agent can run after every deploy.
Not a pentest / limits
Offline only — save the headers first. Grades headers, not TLS or application logic. Not legal advice.
What's included
SKILL.md: workflow, commands, how to explain findingsscripts/: the checker (stdlib Python) plus sharedseccommon.pyreferences/sources.md: specs and guidance citedexamples/: good and bad samples used in the demotests/: unit tests (Python 3.8 / 3.9 / 3.13)
Standard-library Python only. No API keys, no network calls, no installs.
Find more skills like this on the Claude Skills Marketplace, the Codex Skills Marketplace and the Gemini Skills Marketplace, or browse Claude Skills for Security.
- Offline / local files only — does not fetch live URLs or call cloud APIs.
- Heuristic checks; not a full substitute for a professional audit or pentest.
- Not legal advice and not a certification of compliance.
How to use
- 1
Connect your agent to the Agensi MCP
Copy the prompt and paste it into Claude, ChatGPT, Cursor or any agent that supports MCP. It sets up the connection for you. Manual setup
- 2
Sign in to Agensi
Your agent shows a sign-in link. Sign in and click Allow.
- 3
Ask for what you need
Your agent loads this skill and uses it on your task. It always asks before buying a skill.
Reviews
No reviews yet
Be one of the first to try it. Every listed skill goes through the trust checks below.
Security scanned
Checked by our 8-point scan before listing
Fresh listing
Recently published to Agensi
Money-back guarantee
Doesn't do what its page promises? You get your money back.
Trust & safety
Security scan
Security scan passed 20 days ago
Permissions
File Scopes
Fully offline. No subprocess, no network modules used for outbound calls, no credential access.